
At the beginning of the month, Belgium faced a widespread internet outage across the country. Reportedly, the country’s leading internet service provider (ISP), Belnet, was targeted with multiple waves of DDoS attacks that forced nearly 200 organizations, including government websites, to go offline. Incidentally, around the same time, Belgium’s National Security Council (NVR) was finalizing the country’s Cybersecurity Strategy 2.0, whose first version was introduced in 2012 and implemented in the preceding year. The original strategy, which contains 11 of the 15 strategic goals of the European Union Agency for Cybersecurity (ENISA), has been renewed to add six more specific areas that it will concentrate on in the next five years.
Cybersecurity Strategy 2.0: Six Strategic Areas of Focus
Belgium’s various industrial sectors and even SMEs are taking huge strides towards cutting-edge technological adoptions. The country’s cyberspace is continuously evolving and thus the challenges that come with it have evolved too. However, the country has always paid attention to this and invested in securing its cyber front. Cybersecurity is one of the main pillars of their National Plan for Recovery and Resilience, which the government submitted to the European Commission at the end of April.
Cyberthreats are dynamic and require evolving countermeasures. Thus, to take its cyber defenses a notch higher, Belgium’s National Security Council has approved adding and adopting a new and more refined cybersecurity strategy based on six specific objectives:
- Strengthen the digital environment and confidence in it.
- Protect the computers and networks of both, end-users and service providers.
- Protect critical organizations from cyberthreats.
- Raise awareness and educate all stakeholders to tackle all possible cyberthreats.
- Improve partnerships and sharing of expertise between government, industry, and academic institutions.
- Make a clear international commitment concerning cybersecurity.
Miguel De Bruycker, Director of the Center for Cybersecurity Belgium (CCB), who will be responsible for the implementation of this new strategy, said,
The outlined cybersecurity strategy 2.0 aims to make Belgium one of the least vulnerable countries in Europe in terms of cybersecurity by 2025.
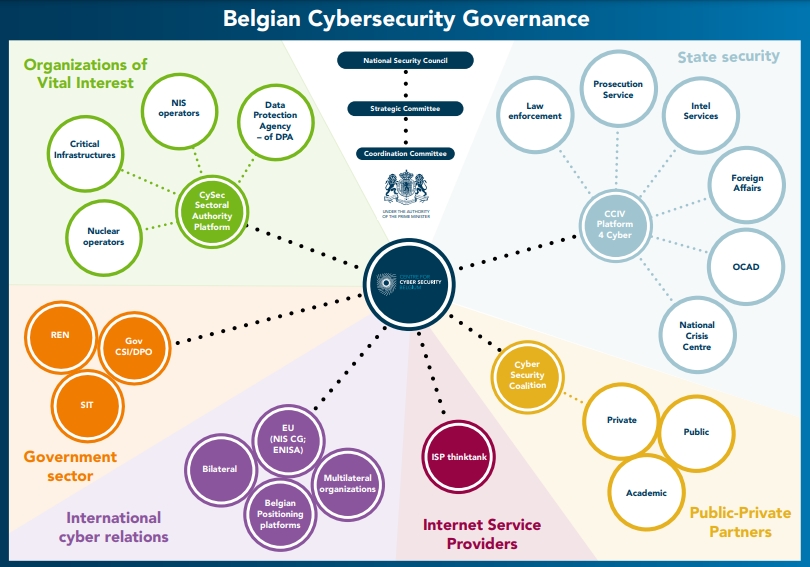
The CCB will work closely with various government services for which cybersecurity is of central importance. A brief overview of Belgium’s cybersecurity governance can be seen in the image below.
Alexander De Croo, the Prime Minister of Belgium, said, “Cybersecurity is not only a priority for Belgium, but also represents a huge opportunity for our companies and SMEs, which have a lot of expertise in this field. We will continue to invest in the protection of our citizens and our systems against cybercriminals and at the same time, we will do everything in our power to develop an ecosystem that promotes innovation in cybersecurity in Belgium.”
Related News:
DDoS Attack on Belnet Takes Down Belgian Government Websites

 has approved the Cybersecurity strategy 2.0 to ramp up its defenses.)