
Threat intelligence firm Group-IB discovered personal records of thousands of users from the U.K., the U.S., South Africa, Spain, Australia, Singapore, Malaysia, and other countries exposed in a multi-stage bitcoin scam. It is found that the attackers used 248,926 sets of stolen personally identifiable information (PII) to pull people into a fake cryptocurrency investment scheme.
According to Group-IB’s investigation, a majority of the victims were from the U.K. with 147,610 records exposed, followed by Australia (82,263), the U.S. (4,147), South Africa (4,149), Singapore (3,499), Malaysia (2,491), and Spain (2,420). While the source of the data leak is still unknown, the researchers stated that the information has been provided to relevant authorities in the affected countries.
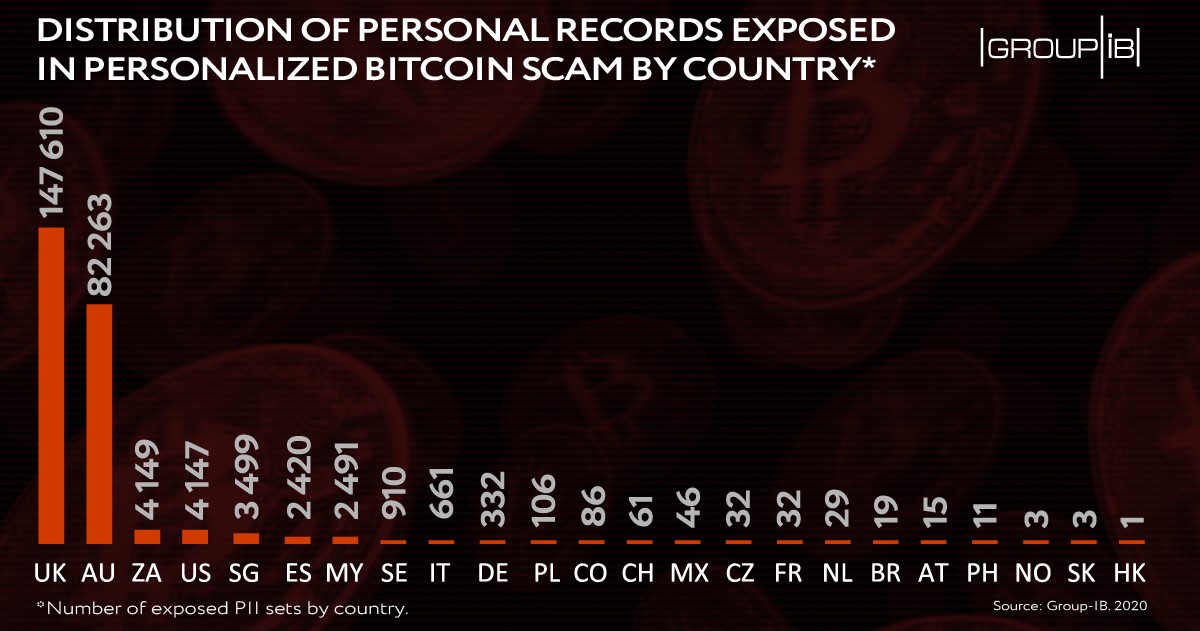
“Victim’s phone numbers, which in most cases came with names and emails, were contained in personalized URLs used to redirect people to websites posing as local news outlets with fabricated comments of prominent local personalities about cryptocurrency investment platform that helped them build a fortune,” the researchers said.
Attack Vector
Group-IB identified all the stages of the attackers’ fraud scheme. Initially, hackers send a phishing message to the victim mimicking a popular media outlet. The message contains a malicious link that redirects the victim to another URL which is designed to trick users into entering their personal information like phone numbers, first and last names, and email addresses.
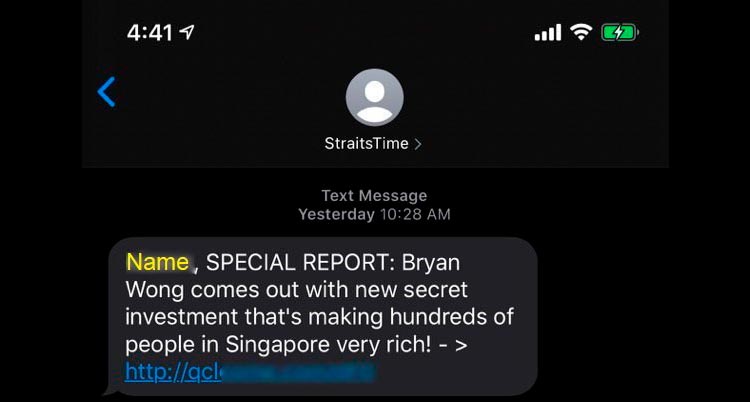
The malicious URLs take users to fraudulent websites that host false interviews and comments attributed to local celebrities saying that they have made a fortune with this new cryptocurrency investment platform. The researchers spotted six fake active domains showcasing the same bitcoin investment platform with different names like Crypto Cash, Bitcoin Rejoin, Bitcoin Supreme and Banking on Blockchain.
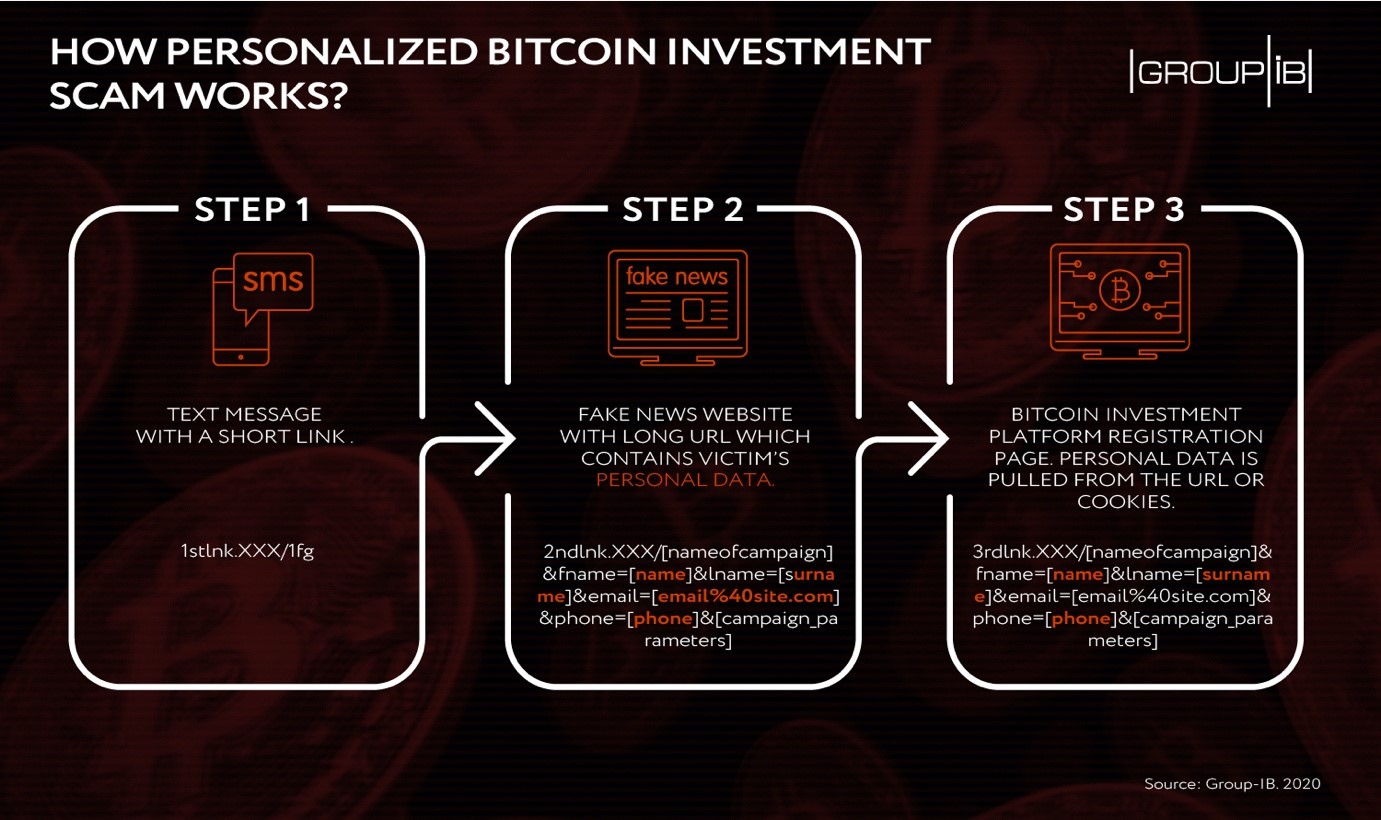
“If a victim decides to click any link in the article, they are taken to a bitcoin investment platform website, where their data, contained in the URL, would already be pre-filled in the registration form without a user’s consent. Later a victim would be asked to add to their account balance in BTC,” the researchers added.
Ilya SachkovIlya Sachkov, CEO and founder at Group-IB, said, “The bitcoin investment scams have been around for quite a while and we regularly detect new instances of crypto fraud. This time however the scheme was significantly upgraded, and a tremendous amount of personal information was leaked. The bad guys got smarter in a bid to increase the success rate of their fraudulent operations. Using personal data allows them to carry out targeted attacks and make a victim’s journey easier and smoother, which levels up the overall effectiveness of the scheme.”

