
Popular security and hacking platform, HackerOne recently announced that it paid ethical hackers $100 million in bounties so far for finding and reporting security flaws in various devices and software via bug hunting programs.
According to Mårten Mickos, CEO of HackerOne, there are around 100 million security vulnerabilities still in the wild, by which cybercriminals can break into systems to steal data, install malware, disrupt vital operations, or distort facts. Mickos stated that HackerOne delivered around 170,000 valid vulnerability reports to its clients and averted more than ten thousand security breaches.
“Hacker-powered security has already made the world much more secure. And with three quarters of a million of ethical hackers signed up, we are making sure we have the capacity to keep finding vulns (vulnerbilities) and helping customers even as the volume of software keeps increasing at a tremendous rate. With a community that size, we represent the creative and inquisitive power of around 65 quadrillion neurons. There is no cybersecurity challenge that a large group of human brains acting towards a common goal cannot tackle,” Mickos added.
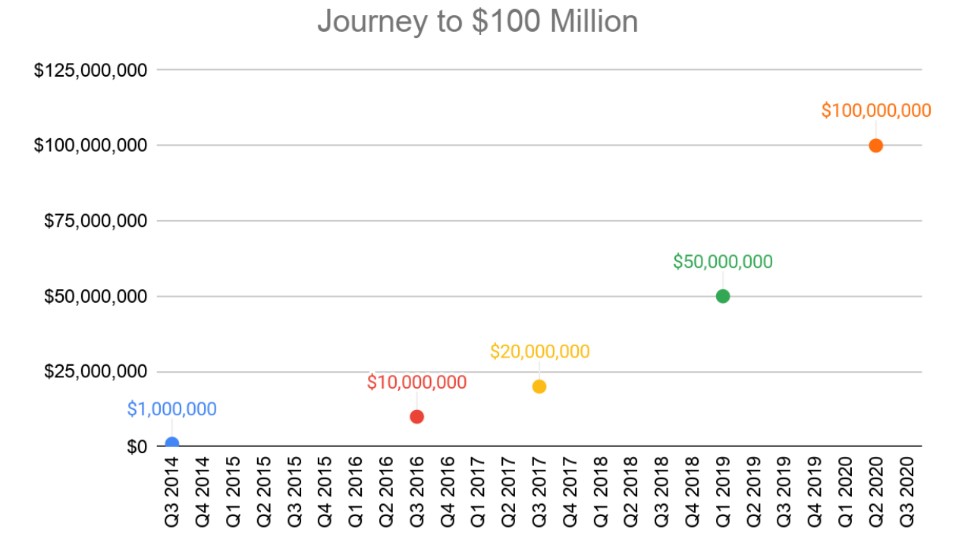
Some Notable Facts about HackerOne:
- 84 new hackers sign up to the HackerOne platform every hour
- Around $6,000 paid in bounties on the platform every hour
- Nearly 214% year-over-year hacker-powered security growth in the federal government
- Around 85.6% growth in total bounty payments, with a 17.5% increase since February when COVID-19 was declared a pandemic
- 343% increase in signups over the past year on Hacker101 – HackerOne’s free online classes for aspiring hackers
- 38% increase in average weekly new registrants for Hacker101 since February, when COVID-19 was declared a pandemic
- Over 170,000 number of vulnerabilities hackers have uncovered in nearly 2,000 customer programs
HackerOne stated that it is planning to produce over 500 Chief Information Security Officers (CISOs) from its large team of ethical hackers in the next 15 years. It also predicted that white-hat hackers will earn around $1 billion in bug bounties within five years, protecting private and government entities from persistent threats.

