Home Blog Page 210

Truecaller Denies Data Leak After 4.75 Mn Users’ Info Emerges on Darknet

Truecaller Denies Data Leak After 4.75 Mn Users’ Info Emerges on Darknet

Cybersecurity research firm Cyble reported that unknown hackers are selling personal information of 47.5 million Indian users of Truecaller, a caller-identification app, on darknet forums for $1,000. The leaked data included details like users’ phone number, name, gender, city, carrier, email ID, Facebook account, and telco details.

In its primary analysis report, Cyble stated that the users’ personal details were kept on dark web forums in a categorized format based on state, cities, and telecom carriers. It also found that the exposed data is from 2019.  Cyble said that such leaked data might impact users in India via spam, phishing scams, and identity theft attacks.

“We were sceptical, but considering we have a large number of subscribers and enterprises in India, we decided to go ahead with the validation stage. And soon we realized that we didn’t make a wrong decision,” Cyble researchers said.

On the flipside, Truecaller denied the data breach allegations claimed by Cyble. “We were informed about a similar sale of data in May 2019. What they have here is likely the same dataset as before. It’s easy for bad actors to compile multiple phone number databases and put a Truecaller stamp on it. By doing that, it lends some credibility to the data and makes it easier for them to sell,” Truecaller said in a media statement.

The Swedish caller identity app is popular among the Indian users. The app provides a set of features to smartphone users including call-blocking, flash-messaging, caller-identification, call-recording, and Chat & Voice services.

Vulnerabilities in Truecaller App

Earlier, researchers discovered a security flaw in the Truecaller app that could expose sensitive users’ data, location, and system information to attackers. The flaw came to light after an India-based security researcher Ehraz Ahmed reported the issue. In a video post, the researcher described how a malicious link can be injected as a profile URL to potentially target attacks on users clicking on the profile. According to Ahmed, the malicious script will get executed without user consent. “The flaw could allow attackers to mount serious attacks on target machines, although this was not the scope of the proof of concept and has been played down by the company,” Ahmed said in a statement.


Building Pro-Active Security Hygiene Helps in Preventing Ransomware Attacks: Microsoft

Building Pro-Active Security Hygiene Helps in Preventing Ransomware Attacks: Microsoft

Threat actors have reinvented their attack approaches during the ongoing COVID-19 outbreak. Several new cybersecurity scams and ransomware activities have risen during the pandemic. According to the Microsoft Threat Protection Intelligence Team, cybercriminals have been using the current situation to gain information from organizations to plan future attacks. The team said that they have observed multiple hacking groups activating dozens of ransomware deployments in the first two weeks of April 2020.

“These attacks can even be fatal, given their impact on aid organizations, medical billing companies, manufacturing, transport, government institutions and educational software providers. However, despite this global crisis, ransomware groups seem to give little regard to the critical services they impact,” Microsoft said in a post.

Vulnerable Systems Are First Targets

Microsoft’s Security Intelligence and Detection and Response team stated that attackers infiltrate target networks and then wait to monetize their attacks by deploying ransomware. To gain access to target networks, threat actors exploited internet-facing systems that had weaknesses such as a lack of multi-factor authentication (MFA). Hackers also preyed on older Windows platforms which were not updated, had weak passwords, or systems with specific existing vulnerabilities. Microsoft observed that hackers used the same techniques in all human-operated ransomware campaigns including initial access, credential theft, lateral movement, and persistence.

Microsoft recommends certain investigation procedures to prioritize if an organization is hit by a cyberattack, these include:

  • Investigate affected endpoints and credentials
  • Isolate compromised endpoints
  • Address internet-facing weaknesses
  • Inspect and rebuild devices with related malware infections

Building Pro-active Security Hygiene

As cybercriminals continue reinventing their attack approaches to compromise new targets, organizations are taking proactive measures to handle the risks.  Microsoft suggested some measures to make networks more resilient against evolving threats, these include:

  • Apply an Account Lockout Policy so that someone who attempts to use more than a few unsuccessful passwords logging onto the system will be blocked.
  • Ensure good perimeter security by patching exposed systems and applying mitigating factors, such as MFA or vendor-supplied mitigation guidance, for vulnerabilities.
  • Utilize host firewalls to limit lateral movement and prevent endpoints from communicating on TCP port 445 for SMBs. This can significantly disrupt malicious activities.
  • Turn on cloud-delivered protection for your antivirus product to cover rapidly evolving attacker tools and techniques. Cloud-based machine learning protections block a huge majority of new and unknown variants.
  • Follow standard security baselines guidance for all your software. A tool like Microsoft Secure Score can also assist in measuring your security posture and recommending actions for improvement, guidance, and control.
  • Turn on tamper protection features to prevent attackers from stopping security services.
  • Turn on attack surface reduction rules, including rules that can block ransomware activity.

“What we’ve learned from the increase in ransomware deployments in April is that attackers pay no attention to the real-world consequences of disruption in services that their attacks cause, even in this time of global crisis. Organizations shouldn’t expect hackers to be concerned about anything other than disruption and potential financial reward, regardless of the impact on people or society as a whole,” Microsoft added.

Organizations must be prepared with the latest preventive actions to protect themselves from evolving threats and safeguard their valuable information.


Five Key Cybersecurity Concerns Amid COVID-19

cybersecurity

The COVID-19 pandemic has disrupted global health, the economy, and social systems. From emptying office spaces to dispersing the workforce, corporates have yet ensured seamless delivery of services. However, remote work environment has also led to a surge in unseen threats in the digital space. Threat actors are prying on potential victims to deploy cyberattacks on home and public networks.

By Pooja Tikekar, Feature Writer at CISO MAG

Corporates are addressing several cybersecurity concerns to protect personal data and information systems. Some of the key concerns include:

1. Security of Remotely Located Devices

The drastic shift to remote working has led to a rise in the use of personal devices for business operations. Leaving sensitive data and work-related documents on unsecured devices could result in data leaks. According to a study from HiveIO, nearly 85% of organizations anticipate a larger remote workforce will threaten operations because of new risks, while 22% fear an increase in business costs to support remote staff. IT teams are undertaking security measures to protect computers from malware.

2. Weak Remote Access

Now that employees are working from home, security professionals need to ask: How many employees use company VPNs when working from home? According to a survey conducted by CISO MAG, only 70% of respondents stated that they were using company VPNs to securely log into the company network. Corporates need to encourage all employees to use VPNs for a secure connection, as communication through a home or public networks could pose a greater risk as they are carried over untrusted networks. It could also result in the exploitation of client and user credentials to collect sensitive data. It is essential for security teams to deploy secure multi-site remote access servers dispersed at various geographic locations.

3. Improving Incident Response and Cyber Hygiene

According to a study conducted by Barracuda Networks, almost half (46%) of global businesses have encountered at least one cybersecurity incident since shifting to a remote working model. Security teams are advising remote employees to maintain good cyber hygiene and asking them to keep their devices up-to-date, patched, and protected. Organizations need to ensure they have a best-in-class remote patch management solution to overcome a security breach. Implementing two-factor authentication (2FA) where possible will also go a long way in preventing data breaches.

4. Cyber Risk Mitigation

Phishing emails sent in the name of the World Health Organization (WHO) continue to be popular among hackers and cyber scammers. To mitigate cyber risks such as phishing campaigns, third-party apps, and malicious adverts, CERT-In has published an advisory urging security teams to stress the avoidance of clicking on links and attachments in email. IT administrators are also advised to monitor outgoing traffic to prevent cyber infections from occurring.

5. Amendment to Business Continuity Plans

Since employees started working from home, the Zoom videoconferencing app found itself millions of users. Unfortunately, its popularity led to increased cyber risks such as password theft. Cyble was the first cybersecurity firm to discover Zoom credentials being stolen and sold on the dark web. It found more than 500,000 Zoom accounts on hacker forums. To avoid the recurrence of such threats, organizations are now devising a holistic business continuity plan (BCP) and making amends to their standard operating procedures (SOPs) for work-from-home employees through a company-specific communication channel or other channels such as MS Teams, Google Meet, and Skype.

Conclusion

Considering all the above concerns, loss of a client or organizational data cannot be risked in the current uniquely challenging environment. It is a crucial time for organizations across all industries to be alert and address the adequacy of their cyber policies.


About the Author

Pooja Tikekar is a Feature Writer, and part of the editorial team at CISO MAG. She writes news and feature stories on cybersecurity trends.

More from the author.


75% Of Security Pros Say Remote Work Led to Changes in Financial Services Cyber Programs: Survey

75% Of Security Pros Say Remote Work Led to Changes in Financial Services Cyber Programs: Survey

An opinion poll from the Financial Services Information Sharing and Analysis Center (FS-ISAC) revealed that 75% of cybersecurity professionals in financial institutions across the globe made sudden changes to their firm’s cybersecurity programs to deal with remote working conditions.

The survey revealed that 11% of respondents said third-party risk concerns led to dramatic changes in their cyber programs. 46% reported their financial institution are likely to invest more in cybersecurity, post-pandemic. Digital banking tools were ready to securely handle a huge increase in volume as only 3% percent of respondents saw these tools driving significant program changes.

FS-ISAC is a non-profit organization responsible for cyber and physical threat intelligence analysis and sharing for the financial and banking institutions. Organizations across the globe leverage FS-ISAC’s intelligence platform, resiliency resources, and network of security experts to anticipate, mitigate, and respond to cyberthreats.

FS-ISAC polled 871 cybersecurity professionals from financial institutions from more than 50 countries, including the U.S., Canada, Brazil, U.K., India, and Singapore. The opinion poll evaluated which trends driven by the pandemic had the most impact on their cybersecurity programs.

Steve Silberstein, CEO of FS-ISAC, said, “The accelerated shift to remote work has fueled a rapid evolution of the cyber threat landscape. As the effects of this pandemic continue to unfold, CISOs and cybersecurity teams are constantly adapting their cybersecurity programs to meet a new reality that is everything but normal.”

Financial Organizations – Hackers Prime Target

A recent study from the cybersecurity firm Intsights revealed that the banking and financial sectors were hit with a constant stream of cyberattacks when compared to other sectors. According to the Intsights report titled, “Banking & Financial Services Cyber Threat Landscape”, around 25.7% of all malware attacks last year was targeted on banks and financial organizations. The study also exposed that the number of data breaches reported in Q1 2019 doubled to any of the quarters of 2018.

Another study from cybersecurity firm Keeper Security stated that lack of cybersecurity resources and strategies lead to an increase in the number of cyberattacks on financial institutions. It is found that 69% of financial organizations globally have suffered a cyberattack in their lifetime. While half of the organizations reported experiencing an attack in the last 12 months.


3 Digital Transformation Shifts Amid Global Uncertainty and How to Handle Them

Digital transformation, security transformation

For most organizations undergoing digital transformation (DX), was already a challenging, complex, and costly journey, and it just got a dose of rocket fuel from COVID-19. The remote workforce has exploded in size seemingly overnight, networks are rapidly changing, and employees, applications and trust zones are more distributed than ever.

By Karl Van Den Bergh, Chief Marketing Officer, Gigamon

As a result, we’re seeing increased pressure on existing IT systems that were never designed for this scenario, as well as an expanded attack surface. And as businesses ask their employees to do more with less amid economic uncertainty, simultaneously, network operations and security teams face the challenge of lowering risk and removing blindspots as traffic patterns change — all while maintaining network performance, security and a positive end-user experience.

The next five years in digital transformation must now happen in the next five weeks. Below I’ve outlined three DX shifts happening in the midst of today’s global workplace transition to remote work and how to handle them. While our current situation will be fluid for some time, what is here to stay is the need for performance and security in a rapidly shifting network, with an eye toward cost containment.

1. WFH requires rapid scaling of remote access infrastructure. On average, organizations have 59% more East-West traffic than North-South. New work from home (WFH) policies are driving the entire LAN traffic base to VPN and have left IT teams with little time to scale their remote access infrastructure for employees. As they scramble to bring remote working capacity online quickly, by repurposing older or existing infrastructure, issues such as failures and bottlenecks can arise in the new network segments and infrastructure. Detecting these issues in a timely manner is critical. But with already stretched resources, these issues become a truly significant challenge.

a. Pro tip: During this transition, with even more changes pending, having accurate visibility into your traffic profile is critical. You need visibility into exactly what’s happening in your network, so you never miss an opportunity, for example, to do accurate capacity re-planning, identifying critical traffic and optimizing bandwidth usage. Networks need to run smoothly, even with a multitude of moving parts.

2. Apps are suddenly pushed to the limit. Customers are now engaging with companies mostly through mobile applications or online. As new application containers, microservices and virtual machines are being stood up rapidly to meet sudden growth in user demand, IT and infrastructure teams risk being left behind by fast-working DevOps and applications teams. This mismatch in alignment can have serious consequences. While application capacity may ramp up, infrastructure capacity may lag and network bandwidth issues, reduced user experience, and application and data access or usage may not be monitored adequately for threats.

a. Pro tip: To achieve the best possible customer and user experience for digital apps, it is important to monitor and visualize application usage and user experience, and take action based on the performance and behavior of these applications. For example, surges in video conferencing traffic due to the intensive use of applications like Cisco WebEx, GoToMeeting, Skype and Zoom can very quickly overwhelm intrusion detection methods. IT teams must be able to quickly visualize which applications are causing these traffic surges, decide whether to analyze this traffic and at what depth, and then filter out safe or low-risk traffic to preserve bandwidth for other applications.

3. When organizations turn inside out, it demands borderless security. Organizations are turning inside out, meaning user traffic previously inside the firewall is now flooding in from outside. Any additional network user activity in new network segments can become a source for threats, such as data leakage or ransomware. Bad actors are quickly exploiting the prevailing paranoia and uncertainty in an effort to compromise users’ systems. These threats use droppers, which are then used to download additional malware on users’ systems to compromise credentials, ultimately leading to ransomware attacks, and potential data exfiltration.

Compounding the inside out challenge is that remote workers use their home network and/or personal devices for work. And it’s not certain that every worker is following recommended security protocols. Even the mandated use of VPNs may not solve the problem, especially if endpoints have not been recently patched. As an example, vulnerabilities are being found and reported in various VPN and firewall manufacturers, which allow Mirai botnet–type variants to take control.

a. Pro Tip: In an effort to ramp up capacity, enterprises need to make sure that if they are using older gear, it is fit for purpose and can be patched and secured. Also, the need for a Zero Trust approach to the network is greater than ever. You need every corner of your network illuminated to provide better visibility and threat detection.

As IT and security teams race to support a remote workforce that is two to three times larger than was ever planned, borderless security needs to be maintained as network traffic has turned from the inside out, not to mention that the applications we depend on are all being pushed to previously untested limits. Visibility and infrastructure agility have become key success factors in an organization’s ability to respond to these challenges, both now and as they continue to manage massive DX shifts as we hurdle toward the new tomorrow.

About the Author

Karl Van Den BergKarl Van Den Bergh is the Chief Marketing Officer at Gigamon. He is a Senior GTM and Product Executive focused on Data and Cloud, with a passion for making a difference by building great teams, products, and businesses. He has a history of successful roles, both strategic and operational, in early-stage startups as well as $1B+ high-tech companies, with extensive international experience.

Disclaimer

CISO MAG did not evaluate/test the products mentioned in this article, nor does it endorse any of the claims made by the writer. The facts, opinions, and language in the article do not reflect the views of CISO MAG and CISO MAG does not assume any responsibility or liability for the same. CISO MAG does not guarantee the satisfactory performance of the products mentioned in this article.

70% Of Mobile and Desktop Apps Contain Open-Source Security Flaws: Report

cyberthreats, bug

According to Veracode’s annual report, 70% of mobile and desktop applications that are being used today have at least one security flaw which stems from the use of open-source library. The report, “State of Software Security,” revealed that lack of awareness about where and how open-source libraries are being used are major factors in contributing toward security issues. Open-source library is free to use centralized code repositories that provide ready-made applications for developers. These libraries are not only ubiquitous but also risky, the research stressed.

The research examined 351,000 external libraries in 85,000 applications and found that these libraries have several security bugs. Even a single bug can affect hundreds of applications. According to the report, the majority of the open-source flaws found in applications like Swift, .NET, Go, and PHP. Swift has specialized use in the Apple ecosystem and has the highest density of flaws. It also has a low percentage of flawed libraries in terms of volume while .NET has the lowest percentage of flawed libraries out of the four, and on a volume it is more than 17 times larger than Swift.

Around 47% of the flawed libraries in applications are transitive i.e. they are not pulled in directly by developers. This means that developers are introducing much more code, and often flawed code, than they might be anticipating.

Veracode also found that Go has a high percentage of libraries with flaws, but an overall low number of flaws per individual library. And PHP has a higher rate of flawed libraries than Go – but more than double the density of flaws in any given library. The report also found that cross-site scripting (XSS) is the most common vulnerability category found in open-source libraries, followed by insecure deserialization (23.5%) and broken access control (20.3%).

“Prominent in almost every application today, open-source libraries allow developers to move faster by quickly adding basic functionality. In fact, it would be nearly impossible to innovate with software without these libraries. However, lack of awareness about where and how open source libraries are being used and their risk factors is a problematic practice,” the report said.

“We found insecure deserialization was a relatively rare flaw among in-house applications. Having such a high ranking when looking at libraries is troubling as this category of flaws can result in unexpected code paths being executed, which means that portions of libraries that we are not even intending to use may be inserted into the execution path of their hosting applications through use of this flaw,” the report added.


India Reports 37% Rise in Cyberattacks in the First Quarter of 2020

Acronis Cyber Readiness Report, cyberattacks in India, cybercrime in India, India’s Private Sector

According to the Kaspersky Security Network (KSN) report, India has witnessed a 37% surge in cyberattacks in  Q1 2020, as compared to  Q4 2019. Kaspersky stated that it detected around 52,820,874 cyberthreats affecting Indian organizations between January to March 2020, while the number of threats detected in Q4 2019  were 40,700,057.

The report highlighted that India ranked 27th globally in the number of threats detected in Q1 2020 when compared to the 32nd position globally in Q4 2019. In addition, India also ranked 11th worldwide in the number of security incidents caused by servers that were hosted in the country, with 2,299,682 security incidents in Q1 2020, as compared to 854,782 incidents in Q4 2019.

It was also found that most users were affected by malware attacks, which are distributed via removable USB drives, CDs and DVDs, and other offline methods. “Protection against such attacks not only requires an antivirus solution capable of treating infected objects but also a firewall, anti-rootkit functionality, and control over removable devices,” the report said.

Saurabh Sharma, Senior Security Researcher, GReAT Asia Pacific at Kaspersky, said, “There has been a significant increase in the number of attacks in 2020 Q1 that may continue to rise further in Q2 as well, especially in the current scenario where we notice an increase in cybercriminal activities, especially in the Asia Pacific region.”

“We see smartphone users being targeted more due to mass consumption and increased digitalization. Risks like data leakage, connection to unsecured wi-fi networks, phishing attacks, spyware, apps with weak encryption are some of the common mobile threats that Android users face,” Sharma added.

“In order to mitigate some of the major risks like data breaches, targeted ransomware attacks, large scale (distributed denial-of-service) DDoS attacks, etc, businesses will need to allocate their budgets correctly to build a stronger security infrastructure,” said Dipesh Kaura, General Manager for South Asia, Kaspersky.

Cyberattacks on Indian Firms

A number of cyberattacks have been reported on organizations in India, causing a huge financial impact on the banks and their users. Recently, security firm Quick Heal Technologies detected a new wave of Adwind Java Remote Access Trojan (RAT) campaign targeting Indian co-operative banks by taking advantage of the COVID-19 pandemic. The company warned that attackers were trying to take control of employees’ devices to steal sensitive data like SWIFT logins. “These banks are usually small in size & may not have a large team of trained cybersecurity personnel, which, potentially, has made them a target for cybercriminals,” Quick Heal said.


Is Samsung’s New Data Security Chip a Game Changer?

Samsung data security chip
Image Credit: Samsung

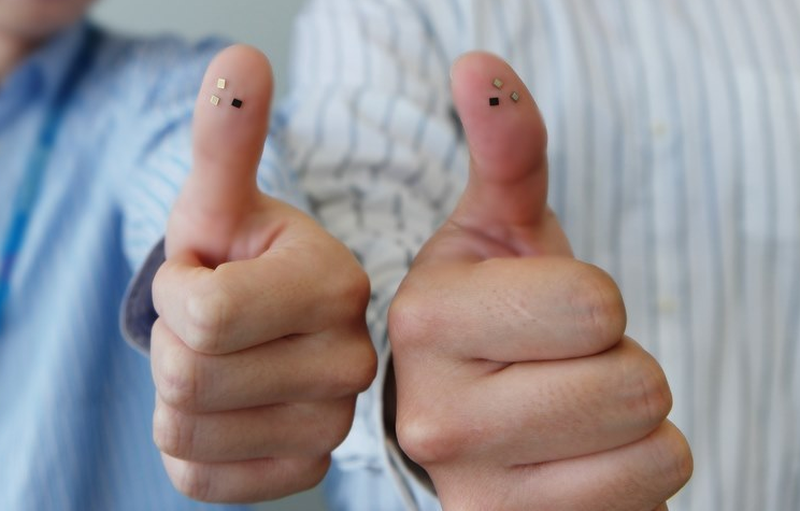
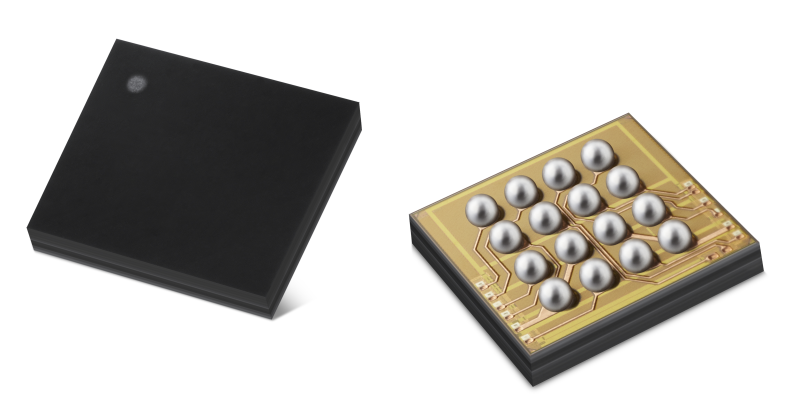
Samsung Electronics, known for its advancements in various turnkey technologies, has now introduced a standalone security solution comprised of a Secure Element (SE) chip (S3FV9RR) that is managed by enhanced security software. This security chip from Samsung offers a secure gateway to perform tasks such as booting, isolated storage, mobile payments, and other applications. Samsung first introduced a SE-chip (S3K250AF) in its S20 device, which had a Common Criteria Evaluation Assurance Level (CC EAL) of 5+. However, with the SE-chip (S3FV9RR), Samsung has taken its own security standards a notch higher as it has achieved a CC EAL certification of 6+, the highest level acquired by a mobile component.

With the new standalone security element solution (S3FV9RR), Samsung is now enabling smart devices to safeguard user’s private information.

Samsung’s Data Security Chip – A Game Changer

The EAL ranking is given by Common Criteria, an organization that certifies the security level of IT products from EAL0 to EAL7, with seven being the most secure. Thus, the CC EAL certification of 6+ is deemed as a game-changer because it is utilized in applications that demand the most stringent security requirements in the market such as high-end smartphones, e-passports, and hardware wallets for cryptocurrency.

Samsung data security chip
Image Credit: Samsung

This new data security chip also supports the following:

  • The hardware-based root of trust (RoT)
  • Secure boot, and
  • Secure device authentication

While running applications on a mobile device, a boot loader initiates a chain of trust, i.e. all the firmware with approved keys is validated sequentially. This boot process is carried out by the RoT, which guards the device against any possible malicious threats and unauthorized software updates.

Dongho Shin, Senior Vice President of System LSI marketing at Samsung Electronics, said, “In this era of mobility and contact-less interactions, we expect our connected devices, such as smartphones or tablets, to be highly secure so as to protect personal data and enable fintech activities such as mobile banking, stock trading, and cryptocurrency transactions. With the new standalone security element solution (S3FV9RR), Samsung is enabling smart devices to safeguard private information.”

This is not the first attempt of hardware-based security and security chips were introduced earlier.

Google’s Titan M Security Chip

Google’s Titan M is an enterprise-grade security chip custom-built for Google’s smartphone brand, Pixel. This chip secures the most sensitive on-device data and operating system. Titan M helps the bootloader (the program that validates and loads Android when the phone turns on) — make sure that the latest Android version is loaded. It stores the last known safe Android version and restricts attackers from moving to an older and potentially vulnerable Android version on the device. Titan M also prevents attackers’ attempts to unlock the bootloader.

The other salient features of Titan M are:

  • Lock screen and On-Device Disk Encryption protection
  • Secure Third-Party App Transactions
  • Insider Attack Resistance

In 2019, Google announced a $1.5 Mn bug bounty reward for cracking Pixel’s Titan M secure element chip. The reward amount though is at the discretion of the rewards committee and depends on several factors.

Trusted Platform Module

In 2009, a computer industry consortium called Trusted Computing Group created a specification for Trusted Platform Module (TPM). TPM, also known as ISO/IEC 11889, is an international standard for a secure cryptoprocessor, a dedicated microcontroller designed to secure hardware through integrated cryptographic keys. A TPM chip has a unique RSA key burned in and a computer program can use a TPM to authenticate hardware devices. In this way hardware-level security complements software-based security, further strengthening the security of the system.

Any application can use a TPM chip for:

  • Digital rights management
  • Protection and enforcement of software licenses
  • Prevention of cheating in online games

3 Hacking Forums Hacked! Database Leaked Online

zero-day vulnerabilities

This might be a case of tasting one’s own medicine. Hackers turned against their own when they leaked databases from hacking forums. Researchers from security firm Cyble discovered database leaks of three hacking forums – Sinful Site, SUXX.TO, and Nulled. According to the researchers, the databases have been exposing hackers’ personal information from the beginning of May 2020. Hacking forums are the places of aggregation for cybercriminals to participate in general discussion with other hackers to share and sell data leaks, hacking tools, malware, and tutorials, etc. Threat actors can easily buy and own malware and ransomware via hacking forums and dark web market networks.

“All these hacking forums are based on general discussion and sharing of related resources. It is a place where users can find lots of great data leaks, hacking and cracking tools, software, tutorials, and much more,” Cyble said in a statement.

The researchers stated that the databases of hacking forums SUXX.TO and Nulled contained detailed information of their users, which appears to be dumped on May 20, 2020. And the database of Sinful Site includes private messages of hackers in the forum, which appear to be dumped on May 15, 2020. While the members behind the database leak are unknown, Cyble stated the websites of the three hacking forums were taken down temporarily.

 Cyberattacks on Hacking Forums

Recently, a database of an infamous darknet forum “WeLeakData.com” was breached, exposing private messages of malicious actors who used the site. Cybercriminals used WeLeakData.com for discussing, trading, and selling databases that are stolen during breaches and combo lists used in credential stuffing attacks. Researchers from Cyble stated that WeLeakData.com site was suddenly brought offline for unknown reasons in January 2020. It was rumored that the operator of this platform got arrested and that the forum database had been stolen or sold to another hacking group. A month after WeLeakData.com was closed, the content of its database, including hackers’ private messages were kept for sale on the dark web.


APAC Public Cloud Spending Increasing, but Businesses May Be Vulnerable: BCG Study

public cloud

A new eight-nation APAC study conducted by Boston Consulting Group (BCG) shows that spending on the public cloud and related services is growing, yet organizations aren’t confident about the security of cloud infrastructure and are holding back. The study titled “Businesses in Asia-Pacific Can Find Resilience and Growth in the Cloud,” showed that APAC cloud spending is growing at a compound annual rate of 25%. This is much faster than similar growth across the U.S. and Western Europe and points to the region’s readiness to invest in cloud initiatives that are accelerating the pace of innovation, growth, and customer engagement. The study notes that capturing the full potential of the cloud may help companies successfully navigate through the current and post-COVID-19 environment. Remote working is accelerating cloud adoption, but companies need to evaluate their security posture for remote environments.

The April 2020 BCG study was developed in collaboration with Amazon Web Services (AWS) and covers Australia, India, Indonesia, Malaysia, the Philippines, Singapore, Thailand, and Vietnam. It shows that companies in these countries are dedicating an average of roughly 5% of their IT budgets to cloud expenditures, a figure that is expected to double by 2023. The study finds that growth in the public cloud could have a positive economic impact of more than $450 billion across the region. It highlights the case of Australian Airways, which saved $40 million per year in fuel costs by using cloud-based analytics to improve thousands of flight routes.

Luc Grimond, a Managing Director at BCG, said, “We’re seeing in the current COVID-19 crisis that more companies are shifting workers to virtual environments and employing end-user computing, using the cloud to quickly roll out essential collaboration tools. Cloud investments will have longer-term benefits as well, such as risk reduction, the ability to provide new and better services to business stakeholders, and improved personalization of product and service offerings.”

Cybersecurity Concerns

Despite the growth in cloud spending, several organizations are slow to move to cloud or are holding back due to security concerns.

Security awareness has also created uncertainty. In some countries, organizations are still awaiting the completion of regulatory assessments governing data privacy and security protection. Companies may also be unaware of the security capabilities offered by their cloud providers. As a result of cybersecurity concerns, approximately 45% of respondents said that they do not host specific data on the public cloud.

Rethink cybersecurity for the cloud. Many nascent businesses still rely on conventional security controls to manage their cloud environments, but these do not provide the necessary safeguards. Mapping out rules and requirements ahead of time is crucial. One executive at a Singaporean financial institution said, “People are biased toward hardware security because it is tangible. We need to assure people that even if the cloud-based hardware is not under their control, it is more secure than the same hardware on premise.”

Remote working is accelerating cloud adoption

With more employees working remotely, companies have moved aggressively to establish virtual work environments. The pressure to move quickly, however, means many businesses are deploying tools that lack adequate data management protection or that are not adapted to existing security processes. As a result, businesses may be exposed to massive security vulnerabilities. Since the COVID-19 pandemic began, for example, the number of cyberattacks on companies globally has risen exponentially as malicious actors introduced new attack vectors, such as the “Co-VID-19” phishing scam. Companies need to review their existing data protection model and security controls to enable fast adoption of cloud-based systems. Accelerating the shift to the cloud would allow businesses to provide remote environments that maintain appropriate data security.

Many advanced cyber solutions exist to help organizations boost their security posture. For example, an Australian bank deployed a fully managed intelligent threat detection service that continuously monitors account activity for malicious or unauthorized behavior to help protect cloud workloads and safeguard customer data.

Many cloud providers also embed sophisticated security protections, such as automated security controls and access provisioning, into their offerings. A financial underwriting company in India found that the cloud security offered by its public-cloud operator included several audit-friendly features that could help the company meet a number of payment, security, and technical compliance standards.