
Security experts from Trend Micro uncovered an ongoing phishing campaign spreading fake Office 365 password expiration reports to compromise email accounts of C-Suite executives. The campaign has been active since 2019. In an official release, Trend Micro stated that the phishing campaign has targeted multiple organizations in the finance, government, real estate, manufacturing, and IT sectors in several countries like Japan, the U.S., the U.K., Canada, Australia, and Europe.
“We found over 300 unique compromised URLs and 70 email addresses from eight compromised sites, including 40 legitimate emails of company CEOs, directors, owners, and founders, among other enterprise employee targets. We are now working with the respective authorities for further investigation,” Trend Micro said.
Leveraging Compromised Infrastructure
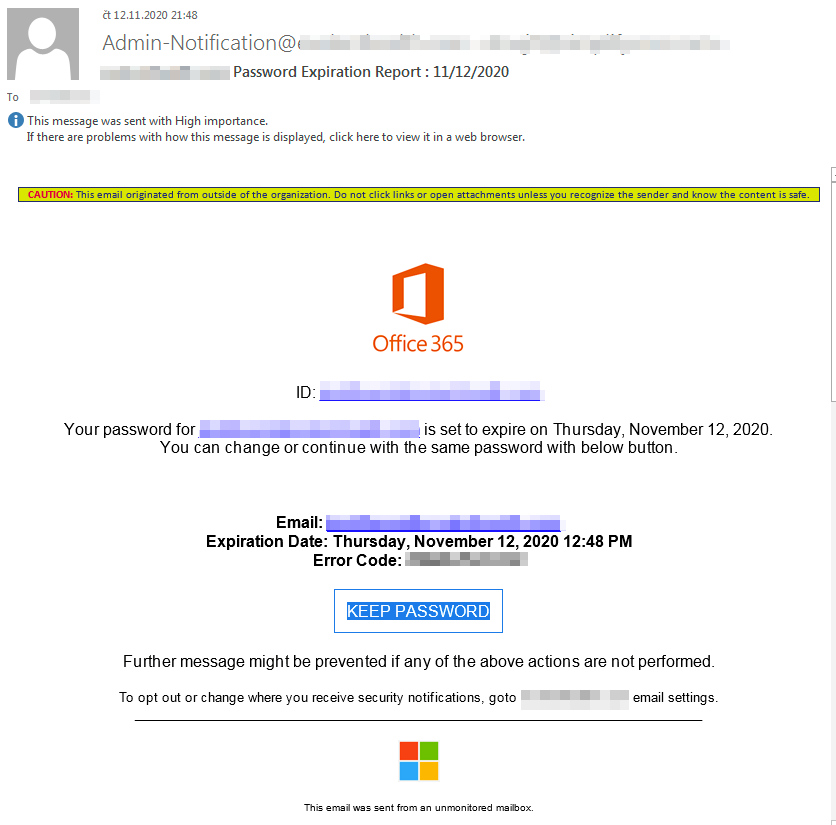
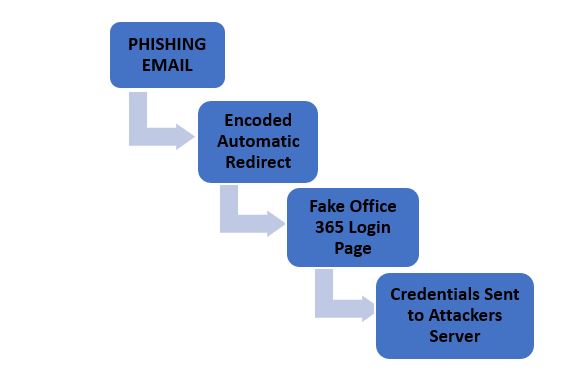
The attackers targeted unsuspecting victims with emails attached with fake Office 365 password expiration reports to trick them into clicking the embedded link in the email. The email prompts the users to click on the “Keep Password” option if they want to continue using the same password. Once clicked, the option leads the user to the phishing page, which asks the user to enter login credentials.
Trend Micro researchers also found several advertisements of malicious actors selling account credentials of CEOs, CFOs, and other C-suite executives in multiple English- and Russian-speaking underground darknet forums. “The attackers are reusing compromised infrastructure and victims’ account credentials to host phishing pages and gain more victims. The kit, which is available for sale, can validate the credentials’ details and accuracy once the victim interacts with the embedded link,” Trend Micro added.

