
Security researchers from Kaspersky Lab found threat actors exploiting Google Play Store for years to distribute advanced android malware to steal a wide range of sensitive data from users. According to the researchers, a malicious campaign named “PhantomLance” has been targeting android devices with malware and spyware payloads embedded in applications delivered via multiple platforms including Google’s Play Store and other android app stores like APKpure and APKCombo.
“The campaign has been active since at least 2015 and is still ongoing, featuring multiple versions of a complex spyware – software created to gather victims’ data – and smart distribution tactics, including distribution via dozens of applications on the Google Play official market,” Kaspersky said.
Evading Google Security Checks
The researchers found that attackers behind the campaign used sophisticated techniques to constantly bypass the vetting process that Google uses to detect malicious apps. Hackers initially submit a benign version of an app and include the backdoor after the app is accepted by Google.
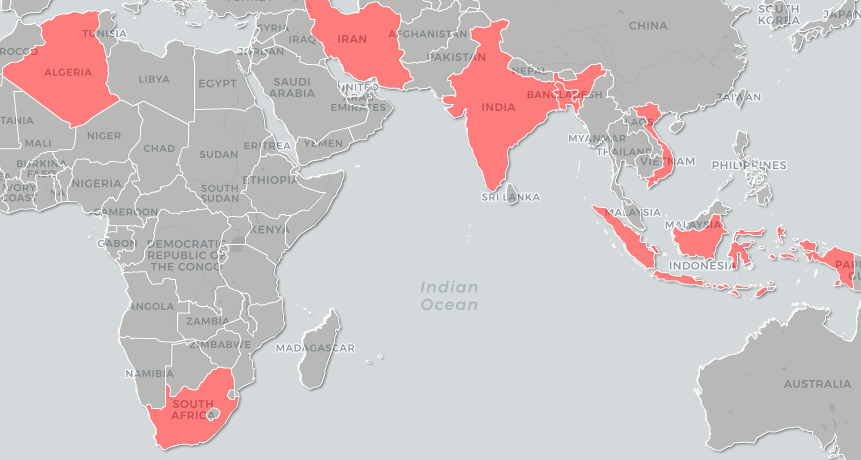
Kaspersky observed over 300 infection attacks on users of android devices in India, Vietnam, Bangladesh, and Indonesia since 2016. There were also several threat detections noticed in Nepal, Myanmar, and Malaysia. Below is a cartographic representation of countries with top attempted attacks.
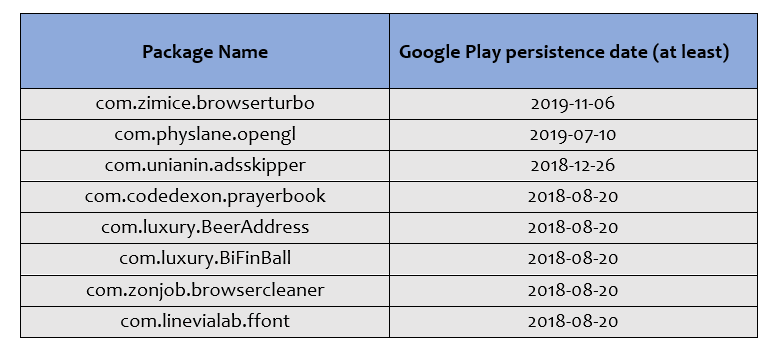
Apart from the android applications containing PhantomLance malware, Kaspersky also provided a list of apps that were distributed and later removed from the Play Store by Google in November 2019.
“During our extensive investigation, we spotted a certain tactic often used by the threat actors for distributing their malware. The initial versions of applications uploaded to app marketplaces did not contain any malicious payloads or code for dropping a payload. These versions were accepted because they contained nothing suspicious, but follow-up versions were updated with both malicious payloads and code to drop and execute these payloads. We were able to confirm this behavior in all of the samples, and we were able to find two versions of the applications, with and without a payload,” Kaspersky added.

