Home Blog Page 255

Patient Data and Medical Images Highly Vulnerable to Leaks: Experts

Medical Devices

Protected patient data, including medical images, accessed through the public internet is a ticking bomb waiting to explode with a data breach. According to TechCrunch, nearly one billion medical images have been exposed online and this is just the beginning. The basis of this revelation comes from a study conducted by Greenbone Networks, a German cybersecurity firm, in September, 2019.

Greenbone carried out an analysis of over 2,300 medical Picture Archiving and Communication Systems (PACS) servers. PACS servers are governed by a standard called DICOM (Digital Imaging and Communications in Medicine). This standard lays the guideline for medical imaging devices that are networked in order to exchange and archive information about patients and images. DICOM makes use of the IP protocol. PACS servers digitally archive medical images (such as X-ray, CT, MRI scans etc.), which can be shared with or accessed by the attending provider from anywhere across the globe.

Of the 2,300 archive systems analyzed by Greenbone, 590 were identified as accessible on the internet. Collectively, they contain over 24 million data records of patients from across 52 countries. There are more than 737 million images linked to this patient data and around 400 million of them are accessible or can be easily downloaded from the internet. In addition, there are 39 systems that allow access to patient data via an unencrypted HTTP Web Viewer, without any protection.

In November 2019, the firm reported that there has been a rise in the number of exposed servers, by more than half, to 35 million patient records, exposing 1.19 billion scans and representing a considerable violation of patient privacy.

Felix Rosbach, Product Manager at comforte AG, said, “The massive amount of data sets combined with the number of freely accessible PACS systems shows that protecting data is still a major challenge for organizations in all verticals. While it is not always possible to prevent malicious access, sophisticated data protection is a must when processing and storing sensitive information–especially Personally Identifiable Information (PII) and healthcare records. These are core requirements of data privacy regulations like HIPAA and GDPR, and there might be fines coming up for this shortly.”

Often, security compliance is managed as a subset of medical compliance, and therefore cybersecurity takes a back seat.

Earlier a data breach at Inmediata Health Group, a Puerto Rico-based health care center, stated that a technical glitch in the webpage settings permitted search engines to expose internal webpages online, which contained patients’ sensitive information. According to Inmediata, the exposed data included patients’ names, addresses, social security numbers, and other personal health information.

Elasticsearch Database Leaks 100 GB Data of Peekaboo Moments App

Thousands of baby videos and images were being left unsecured and exposed online by a mobile app called Peekaboo Moments.

Peekaboo’s app developer, Bithouse, left the Elasticsearch database open and without password protection. The database contained more than 70 million log files comprising nearly 100 GB data stored from March 2019. The exposed data includes detailed device data, links to photos and videos, and around 800,000 email addresses.

Peekaboo stated that it’s still unclear for how long the server has been exposed to the data and who might have accessed it. The data breach news comes even after Peekaboo Moments promised to safeguard the data and information it stores.

This is not the first time Elasticsearch has undergone a server breach. Multiple security incidents were reported on Elasticsearch servers earlier.

Recently, security analysts Bob Diachenko and Vinny Troia discovered an open Elasticsearch server that contains unique data records of around 1.2 billion users. The server holds more than 4 terabytes of data, without password protection or authentication.

The exposed data included names, email addresses, phone numbers, LinkedIn, and Facebook profile information. It’s believed that the exposed data appears to have originated from two different data enrichment companies namely People Data Labs (PDL) and OxyData.Io (OXY).

Earlier, almost everyone in Ecuador became a victim of a massive data breach that exposed the personal information of over 20 million individuals, including the country’s president. Security firm vpnMentor discovered the breach on a Miami-based Elasticsearch server owned by an Ecuadorian company Novaestrat. It’s said that the exposed data appears to have come from various sources, including the Ecuadorian national bank, Ecuadorian government registries, and an automotive association called Aeade.

CRITICALSTART Partners with SentinelOne for Endpoint Protection

Collaboration, partnership, alliance, KnowBe4 and Agari Partner to Prevent Identity-Based Email Attacks

CRITICALSTART, a provider of managed detection and response (MDR) services, recently partnered with endpoint protection firm SentinelOne to jointly develop next-generation endpoint, cloud, and IoT protection security solutions.

Founded in 2013, SentinelOne provides autonomous endpoint protection services to organizations to help them prevent, detect, respond, and hunt attacks across all major vectors. The company claims that its security platform is designed to save customers time by applying AI to automatically eliminate threats in real-time for both on-premise and cloud environments.

CRITICALSTART helps enterprises protect their data systems while reducing their security risks. The company offers a set of security solutions from the delivery of managed security services to security-readiness assessments like the defendable network, professional services, and product fulfillment.

Commenting on the new partnership deal, Randy Watkins, CTO of CRITICALSTART, said,  “We selected SentinelOne due to its efficacy, ease of management, and breadth of EDR capabilities. Additionally, our partnership helps address the growing headcount shortage by giving organizations the resources they need to secure their operations.”

Phishing Scam Affects Texas-Based School District

phishing campaign, Smishing attacks

The Manor Independent School District (MISD) in Texas is facing a loss of US$2.3 million after falling victim to a phishing attack. The phishing scam came to light after a school district employee discovered the issue in December 2019 and reported it to the police.

MISD’s notice didn’t reveal any information about the incident. However, in a notice published on Twitter, the MISD stated that the Manor Police Department and FBI are investigating the incident.  Anne Lopez, a detective with the Manor Police Department, disclosed a few details about the phishing attack to news outlet KVUE.

Lopez said, “It was three separate transactions. Unfortunately, they didn’t recognize the fact that the bank account information had been changed and they sent three separate transactions over the course of a month before it was recognized that it was a fraudulent bank account. So I think it’s important that any email you get, any phone call you get, that you question everything and make sure you know who you’re talking to directly that you look through every part of that email or any information that they’re providing you, and double-check you have checks and balances in place to make sure that any information provided to you is actually accurate.”

School districts have become an easy target for cybercriminals to launch cyberattacks. Multiple attacks have been discovered and reported on schools in recent times. To address the same, two U.S. Senators, Gary Peters (D-Mich.) and Rick Scott (R-Fla.), both members of the Senate’s National Security and Government Affairs Committee, have tabled a new bill called the “K-12 Cybersecurity Act.”

The Act directs the DHS Cybersecurity and Infrastructure Security Agency (CISA) to first study the cybersecurity risks associated with K-12 educational institutions. Once the study is done, CISA will then be responsible to develop cybersecurity recommendations and set up online tools to help schools with their cybersecurity requirements.

“Cable Haunt” Vulnerability Exposes 200 Million Modem Cables to MITM Attacks

Compromised Email Accounts

A security vulnerability named “Cable Haunt,” in Broadcom’s cable modem, exposed around 200 million home broadband gateways in Europe, to remote hijacking attacks.

The flaw, tracked as CVE-2019-19494, was discovered by four Danish researchers – Alexander Dalsgaard Krog, Jens Hegner Staermose, and Kasper Kohsel Terndrup from security company Lyrebirds, along with an independent researcher Simon Vandel Sillesen. The CVE-2019-19494 vulnerability could be exploited by malicious actors by tricking a victim into opening a specially crafted web page, which contains malicious JavaScript code.

According to the researchers, “Cable Haunt is a critical vulnerability found in cable modems from various manufacturers across the world. The vulnerability enables remote attackers to execute arbitrary code on your modem, indirectly through an endpoint on the modem. Your cable modem is in charge of the internet traffic for all devices on the network. Cable Haunt might therefore be exploited to intercept private messages, redirect traffic, or participation in botnets.”

Cable Haunt impacts a standard hardware and software component of Broadcom chips, known as spectrum analyzer, which protects the cable modem from signal surges.

The researchers further added, “The exploitation will be performed in two steps. First, access to the vulnerable endpoint is gained through a browser. Second, the vulnerable endpoint is hit with a buffer overflow attack that gives the attacker control to the modem.”

The attackers can also perform a range of malicious activities including:

  • Change default DNS server
  • Launch remote man-in-the-middle attacks (MITM attacks)
  • Hot-swap code or even the entire firmware
  • Upload, flash and upgrade firmware silently
  • Disable ISP firmware upgrade
  • Change every config file and settings
  • Get and Set SNMP OID values
  • Change all associated MAC addresses
  • Change serial numbers
  • Turn devices into bots for botnet attacks

The History of Security and the Fight to Protect Ourselves

history of computers

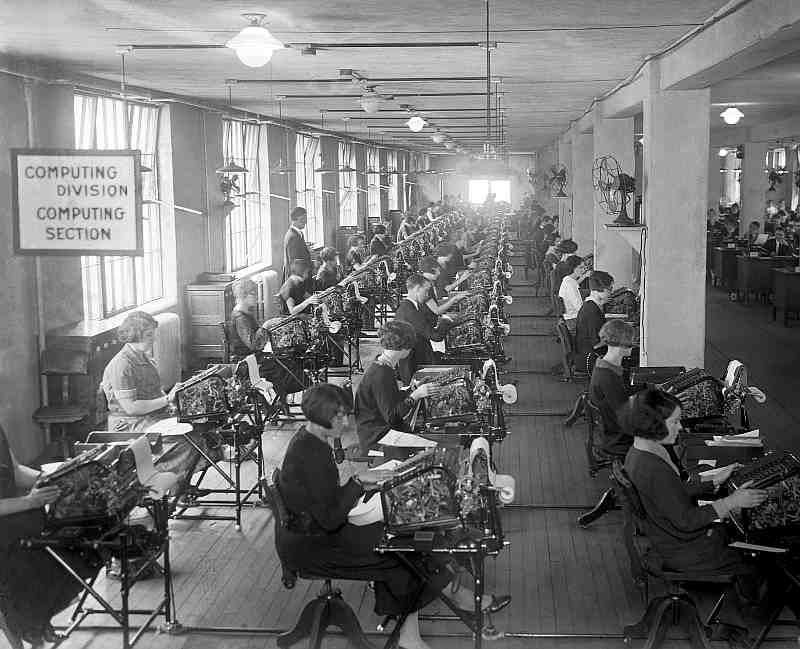
While almost everyone in modern industry has heard and thought about cyberattacks, breaches, data compromises and defenses, cyber warfare pre-dates the modern computing era. As far back as 1976, when I started my first job in astrodynamics working on Air Force satellites, security was an important consideration–decades before the Internet and our powerful computing devices.

By Michael Miora, SVP & CISO, Korn Ferry

The security story I want to share begins in the late 1970s. As a young UC Berkeley graduate, my attention was on mathematics and getting a job! I never imagined that I would focus on security for the next few decades. I never envisioned myself as a critical decision maker, whose actions would affect the course and success of a multi-billion-dollar, global enterprise.

Understanding this security story will help us all be better at identifying what needs to be protected and how we need to define and design our protections.

With a background in mathematics, I opted to study Satellite Orbit Calculation and Manipulation during my first job. However, my attention was quickly captured by the need to protect the information assets of the 70s against our adversary, the then-Soviet Union.

Today, it is obvious that we need to encrypt the large amount of data coming from satellites and going to ground-based receivers. In the 1970s though, such encryption and protection was beyond the capabilities of the small and low-powered satellite computers. Therefore, we needed to solve this problem using innovations that would use the capabilities we had at our disposal.

Scientists in the early satellite industry designed a process of commutation and de-commutation of data; this was an accidental security design. By having each bit of a downstream represent specific information known only to the receiving equipment, we had a de facto secret required to understand the data.

The Major Transformation

In November 1988, we experienced the first major, though ostensibly unintentional, attack on the ARPANET, the predecessor to the Internet. It was the “The Morris Worm,” which exploited known vulnerabilities very similar to those that still plague us today, including weak passwords, lack of filtering, and trusting outside networks without controls.

At the time, I was working for a major defense contractor that was affected by this worm. We formed a rudimentary team to study the attack and plan how to respond to the future attacks we already knew were going to come. Today, we call this a Security Incident Response Plan!

By the end of the eighties, I gathered all the experiences that I gained from my satellite and defense work to launch InfoSec Labs, one of the pioneering security consulting firms that focused on helping major financial, healthcare, and manufacturing companies protect themselves. I thereby entered an environment where my advice needed to be presented and then sold to clients as reasonable and justifiable actions. We all know how difficult it is to convince top management to spend money on intangible rewards and returns. It was challenging but rewarding to provide advice, help implement that advice, and then witness the result.

We built InfoSec Labs from the ground up without external funding because the Venture Capital firms had not yet fully grasped the importance of security or the role it would play in the coming years.

The Holy Grail: Anti-Virus

“I Love You!” Sound familiar? For those who were using email and Microsoft Word in 2000, you probably know the impact of this virus. This was one of the first major and wildly successful attacks in the history of computing, with far reaching effects that dwarfed the Morris Worm. It was very innovative because it was the first use of embedded macros in a trusted program, perverted to malicious use, and it embodied all the “features” of our modern viruses.

It was at this time that I was approached by some well-established security companies. The reputation of my company and my team attracted their attention, and my firm eventually was acquired by Rainbow Technologies, a major, publicly traded security company.

There were already anti-virus programs and systems available, but this helped spur quicker and more widespread implementation of these protections across industries and companies worldwide. The evolution of anti-virus quickened and increased in its sophistication. So did the attackers.

Over the coming years, there were many and varied attacks, ever increasing in their sophistication. Even last year, in 2018, we saw new forms of attacks that recognized the improving protections and worked to circumvent them. Some of those used normal-looking software that launched and encrypted systems (“ransomware”). Others used stealth methods that did not use files to attack and take over systems; still others used other advanced techniques.

Today the original anti-virus has transformed into anti-malware and Endpoint Detection and Response (EDR) which include sophistication unimaginable even a few years ago, with storage of data and interactions requiring terabytes of storage. Cloud strategies along with global regulations and compliance requirements have made us smarter and caused us to work harder. We all know that compliance does not drive security, but smart security achieves compliance and protects us against the attackers.

Are We There Yet?

In 2017 and 2018, every U.S. voter was compromised. Every Hong Kong voter was compromised. Over the past two years, every U.S. adult has had their credentials and credit information compromised (300 million last year). The European Banking Commission has mandated that all banking compromises in EU be reported to them immediately. Twenty-five percent of all Australian companies were compromised last year.

The attackers work just as hard as we do, sometimes with significantly greater flexibility and resources. Often, these resources and protections are provided by nation states that provide immunity from capture and prosecution. It is our job to coordinate better with each other, to share information and to jointly find newer and better ways to protect ourselves. Let’s not be bashful in telling our vendors what we want and suggesting collaboration and cooperation among competitors and complementary products.

I do that with some success. Though the vendors don’t always follow the advice, their attention shifts to include that thinking.

The Goal of Availability

There is a creative tension between meeting security requirements and achieving business goals. Security is not just technical security; it means working securely and with recognition of required operational security considerations. Business goals require a significant dedication to customer service, translated to keeping systems and applications up and running nearly all the time.

The problem is that keeping systems and services always-on may cause the perceived need for availability to overwhelm the confidentiality and integrity required of systems, thereby compromising security. The resolution is to build business requirements to be compatible with security needs. Business needs should be defined in concert with security goals so that, as the business needs grow, security can grow with them.

The fabric of companies is changing to embrace digital marketing, sales, management, human resources, and operations at every level. This is the much-discussed digital transformation. Our business partners in every aspect of business link with us so we share our business DNA, and the very core of our functions with each other. But we also share our weaknesses. Therefore, our security transformations must include our core synergies and our central business nervous systems so that cooperation and alliances increase our strength rather than compromise our corporate immune systems.

The Next Challenge

Our security journey must continue by more closely integrating security with business objectives. We must learn to speak the language of business, and not expect senior executives to learn the language of security.

According to Harvard Business School: “Leadership is about making others better as a result of your presence and making sure that impact lasts in your absence.”

What we do to help the industry and the profession grow, and do better, will be our legacy.

Disclaimer: The facts, opinions, and language in the article do not reflect the views of CISO MAG and CISO MAG does not assume any responsibility or liability for the same.

EKANS aka SNAKE Ransomware Slithers Slowly Through Corporate Networks

ransomware, ryuk ransomware, cox media

After Ryuk and Zeppelin, Snake Ransomware is a new breed of ransomware attack that targets not one or two but all computers on a company’s business network. The Snake ransomware was first discovered by the MalwareHunterTeam and studied by Vitali Kremez, Head of SentinelLabs.

“The (Snake) ransomware contains a level of routine obfuscation not previously and typically seen coupled with the targeted approach,” Kremez told BleepingComputer in a conversation.

Kremez’s analysis found that:

  • Snake Ransomware is written in Golang, an open-source programming language that provides cross-platform support.
  • It removes the computer’s Shadow Volume Copies and terminates various processes related to SCADA systems, virtual machines, industrial control systems, remote management tools, network management software, and more.
  • During encryption, Snake skips all Windows and other system folders on the computer.
  • The encryption process is slower as compared to other ransomware attacks. The attacker also has the provision of choosing the time for encryption. This can potentially allow the network admins to control the damages of the attack.
  • Snake then unusually adds a random five-character string as a suffix to the existing extension name. For example, Test1.jpg file is encrypted and named as Test1.jpgAUxRo. This is unusual as ransomware usually adds specific extensions to the file and not just append the existing extension.
  • In each file that is being encrypted, the snake also appends the “EKANS” file marker. EKANS is SNAKE spelled in reverse order. This is where the ransomware derives its name from.
  • On completion of the encryption process, a ransom note named Fix-Your-Files.txt is generated on the desktop. Here is the text in the Ransom Note:

——————————————–

What happened to your files?

——————————————–

We breached your corporate network and encrypted the data on your computers. The encrypted data includes documents, databases, photos and more –

All were encrypted using a military-grade encryption algorithm (AES-256 and RSA-2048). You cannot access those files right now. But don’t worry!

You can still get those files back and be up and running again in no time.

———————————————

How to contact us to get your files back?

———————————————

The only way to restore your files is by purchasing a decryption tool loaded with a private key we created specifically for your network.

Once run on an affected computer, the tool will decrypt all encrypted files – and you can resume day-to-day operations, preferably with

better cybersecurity in mind. If you are interested in purchasing the decryption tool contact us at [email protected]

——————————————————-

How can you be certain we have the decryption tool?

——————————————————-

In your mail to us attach up to 3 files (up to 3MB, no databases or spreadsheets). We will send them back to you decrypted.

From the text written in the ransom note, it is evident that the attack is targeted at the entire network and not just one or two computers. It also says that encryption algorithms, AES-256, and RSA-2048 have been used in this ransomware attack which means it is difficult to develop a free version of its decryptor.

Australia’s Bushfire Donation Website Hit by MageCart

New Programming Language

Australia has been very much in the news for the huge losses caused by bushfires to humans and wildlife alike. In order to help the people fighting it out on the frontline, many organizations have set up online donation gateways on their respective websites. But the  Malwarebytes Threat Intelligence Team has found a legitimate donation collecting website that has been compromised by a MageCart script.

Hackers planted a MageCart script on the checkout page of the website to steal the payment information of the donors. This information was then sent to a domain controlled by the hackers. The research team confirmed that the software used for skimming is known as ATMZOW. On completing the donation process successfully, the stolen card details were then sent to a website vamberlo.com

Malwarebytes’ Jérôme Segura told BleepingComputer, that once they became aware of the compromised website, they were able to get the vamberlo.com domain shut down.

Since the malignant domain used by the hackers has been shut down, the skimmer is not able to send the stolen card data to the hackers. Still, the hackers can use a new domain to restart this attack using a new domain address. The only way to secure the website completely is to remove the MageCart script. But the malicious code is yet to be removed. The ATMZOW skimming MageCart script has also been discovered on 39 other websites.

Earlier in November 2019, Macy’s, an American department store chain, stated that its customers were hit by an attack that affected countless numbers of credit cards. The retailer stated that unknown intruders planted a card-stealing malware script on its payment site and collected customer details.

According to an official statement, the attackers installed a MageCart script on the checkout page of its website and siphoned off customers’ payment card details between October 7 and October 15, 2019. The compromised data included customers’ names, addresses, phone numbers, credit card numbers, card verification codes, and expiration dates.

Tesla Offers US$1 Million and a Car as Bug Bounty Reward

Tesla avoids cyberattack, tesla zero-click vulnerabilities

Tesla, an American automotive and energy company, announced its bug bounty program by offering US$1 million and a free car to any security researcher who can hack their Model 3 car.

Last year, a security research team named Fluoroacetate won a Tesla Model 3 and US$35,000 for exposing vulnerabilities in Tesla’s infotainment system.

The Elon Musk-owned electric automaker stated that it’s going to be featured in the hacking event Pwn2Own, which will be held in Vancouver in March 2020.

Bug hunting events help companies to test and improve their security systems. According to several cybersecurity experts, Tesla cars are tough to hack.

David Kennedy, the CEO of TrustedSec, said, “Tesla is on the path to be the most secure car. I don’t think that they’re there yet, but I think they’re definitely striving for it.”

Tesla functions more like a technology firm because it is known to have its own operating system. The company periodically sends updates to the customers’ car overnight, including new features (like raising the ground clearance) and security updates.

U.S. Telcos Vulnerable to SIM Swapping Attacks: Princeton Research

SIM Swapping

A study from Princeton University revealed that five major telecommunication providers in the U.S. are vulnerable to SIM swapping attacks.

According to the researchers at Princeton, AT&T, T-Mobile, Tracfone Wireless, US Mobile, and Verizon Wireless were found to be applying insecure procedures with their customer care centers, which could be exploited by attackers to launch SIM swapping attacks. They also tried to trick their customer support into changing a user’s phone number to another SIM without providing proper credentials. It’s said that researchers used 50 SIM cards, 10 with each provider, to call the telco’s customer support.

To quote from the study: “We found that all five carriers used insecure authentication challenges that could be easily subverted by attackers. We also found that attackers generally only needed to target the most vulnerable authentication challenges, because the rest could be bypassed.”

Besides, the research team also evaluated the authentication processes of 140 online services and websites that offer phone-based authentication. The results stated that 17 of the 140 websites were vulnerable and allow a malicious actor to compromise the account with a SIM swapping attack. The Princeton researchers also notified their findings to all the affected companies.

The researchers said, “When providing incorrect answers to personal questions such as date of birth or billing ZIP code, research assistants would explain that they had been careless at signup, possibly having provided incorrect information, and could not recall the information they had used.”

What’s a SIM Swapping Attack?

A SIM Swapping attack is one of the simplest ways for cybercriminals to bypass users’ 2FA protection. In a SIM swap attack, the attacker calls service providers and tricks them into changing a victim’s phone number to an attacker-controlled SIM card. This allows the attacker to reset passwords and gain access to victims’ sensitive data.

In September 2019, Twitter CEO & Co-founder Jack Dorsey’sTwitter account was compromised by a hacking group named Chuckle Squad. Hackers used SIM Swapping Attack technique to take over Dorsey’s account by exploiting the cell carrier vulnerability, which enabled them to post anti-Semitic comments in his account feed. However, Twitter officials clarified that his account is now fixed and there is no sign that Twitter’s systems have been hacked.